

Nasdaq CEO Demands US Strategy as Fraud Hits $579B
Nasdaq chief executive Adena Friedman urged federal lawmakers to establish a unified national counter-fraud plan as global criminal losses reached $579B, calling on telecommunications providers, online social platforms, commercial banks, and intelligence agencies to combine transaction defenses against automated deception syndicates.
Inioluwa Ademidun | · 11 min read
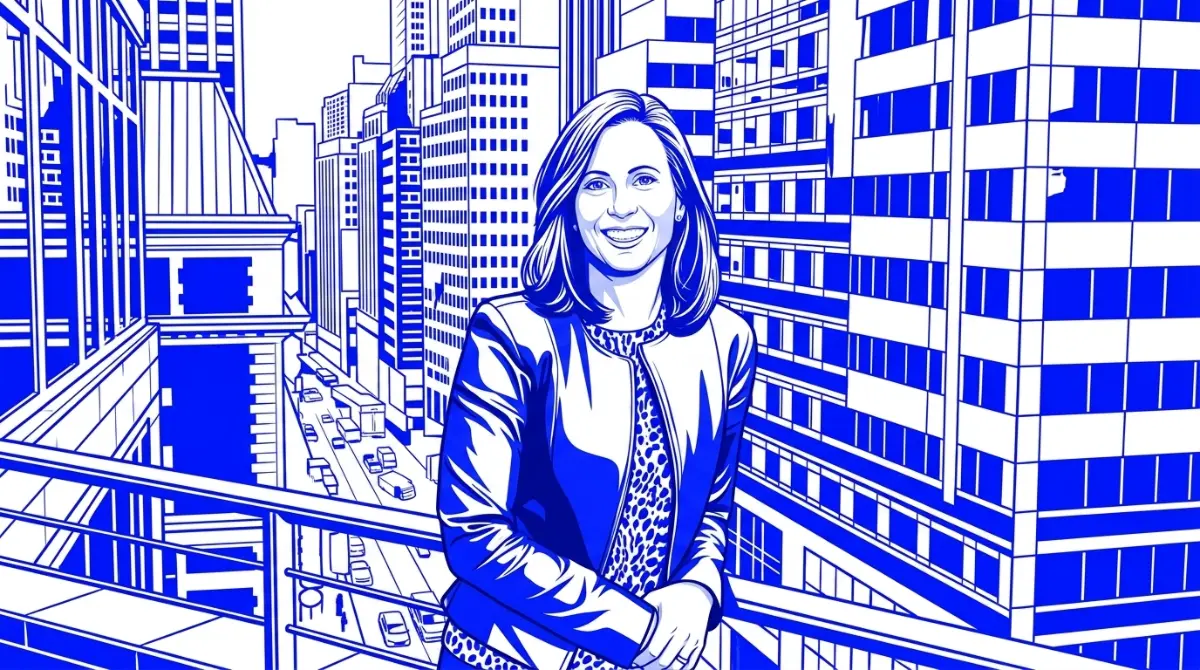
Modern banking fraud operates with the coordination of a sovereign military strike. In past decades, financial criminals spent weeks forging physical signatures on paper cheques or skimming plastic debit cards at gas station fuel pumps. Local police detectives could track physical suspects through bank security tapes and regional pawn shop receipts. That local crime model has been dismantled by organized syndicates operating out of overseas boiler rooms. Criminal enterprises now deploy automated voice cloning tools, forged government identities, and synthetic financial profiles to drain consumer savings accounts and corporate treasury reserves in seconds. On Friday, October 23, 2026, Fortune reported that Nasdaq Chief Executive Officer Adena Friedman issued an urgent call for action from Washington. Speaking before financial leaders and regulatory authorities, Friedman warned that global fraud losses passed $579B annually, inflicting immense economic harm on working households and commercial lenders. The market executive declared that piecemeal defenses by individual banks are failing, demanding a coordinated national defense plan that unites major technology platforms, telecommunications carriers, and federal law enforcement. The warning lands as international banking networks confront synthetic deception, an operational threat examined when Revolut faced data exposures from forged requests.
The scale of the problem is forcing financial exchanges to rethink their responsibilities. Nasdaq is known around the world as an electronic stock market where investors buy and sell shares of Apple, Microsoft, and Amazon. Behind that trading floor sits an expanding security enterprise anchored by Verafin, the financial crime detection firm Nasdaq bought for $2.75B in 2020. Verafin software monitors trillions of dollars in daily money movements across more than 2,500 commercial banks and credit unions. That transaction monitoring gives Friedman an unvarnished view of financial crime trends. Friedman explained that financial institutions are fighting asymmetrical battles: private banks spend billions updating anti-money laundering controls, while criminal syndicates weaponize cheap automation to launch millions of personalized scams every day. Without federal coordination that compels social media networks and telephone carriers to share fraud telemetry before money leaves victim accounts, banking firewalls will remain porous. The struggle to secure corporate finance platforms matches themes we analyzed in our report on Revolut challenging traditional banking giants.
The Industrial Architecture of Pig Butchering and Synthetic Identities
To grasp why fraud losses reached $579B, one must look at how digital deception has been industrialized. The explosion in financial theft is no longer driven by lone hackers operating out of suburban bedrooms. The modern fraud engine is powered by transnational syndicates operating guarded compound complexes across Southeast Asia, West Africa, and Eastern Europe.
These criminal compounds run complex operations known as pig butchering, or sha zhu pan. Thousands of trafficked workers are forced to manage synthetic personas on WhatsApp, LinkedIn, and dating applications. Automated translation software and voice synthesis tools allow operators to build months-long relationships with victims in North America and Europe, convincing individuals to deposit life savings into fraudulent investment portals that display manipulated profit numbers. Once funds are deposited, the money is moved through series of cryptocurrency mixers and offshore accounts, making asset recovery almost impossible. Concurrently, criminal rings manufacture synthetic identities: blending legitimate Social Security numbers with fictitious names and addresses to secure consumer credit cards and personal loans. When these accounts default, lenders write off billions in losses, passing higher borrowing rates down to honest consumers. The technical methods behind synthetic online deception reflect issues we documented when machine tools lowered barriers for digital intrusions.
The Asymmetrical Economics of Automated Attacks
The core challenge confronting financial security teams is economic asymmetry. For a commercial lender, defending corporate infrastructure requires hiring thousands of compliance specialists, paying annual software licensing bills, and maintaining strict legal documentation. Commercial banks spend millions each year to comply with federal Know Your Customer and Anti-Money Laundering mandates.
For criminal syndicates, launching automated attacks costs pennies. Using conversational software tools and automated dialers, a scam ring can send five million personalized phishing messages in minutes. The attackers need only one out of ten thousand recipients to click a malicious link or disclose a one-time passcode to net hundreds of thousands of dollars. When automated tools lower operational expenses for bad actors, attack volumes surge exponentially. Traditional bank rule engines, which flag transactions based on rigid dollar thresholds or geographic anomalies, cannot distinguish between a legitimate customer approving a wire transfer and an elderly victim acting under the emotional duress of a cloned telephone caller. Defensive strategies designed to counter automated intrusions match architectural models we detailed when Armadin secured capital for agent security systems.
Comparing Financial Fraud Losses Across Operating Categories
| Fraud Scheme Type | Annual Global Loss Volume | Primary Digital Infiltration Vector | Primary Target Demographic | Asset Recovery Rate |
|---|---|---|---|---|
| Authorized Push Payment Scams | $180B to $210B | Cloned voice calls & social messaging | Retail banking customers & retirees | Below 8% of stolen funds |
| Synthetic Identity Theft | $95B to $115B | Credit bureau credit-building loops | Auto lenders & unsecured card issuers | Under 3% recovery rate |
| Corporate Wire Interception | $85B to $105B | Executive email compromise & token theft | Mid-market commercial suppliers | 12% to 18% via fast recalls |
| Deceptive Investment Portals | $75B to $90B | Paid search ads & social media promos | Retail cryptocurrency investors | Negligible (under 1%) |
| Account Takeover Actions | $55B to $65B | Credential stuffing & SIM-swap exploits | Online brokerage & payment accounts | 20% to 25% via account freezes |
The comparative data illustrates why Friedman focused on authorized push payment fraud as the most destructive financial crime of the decade. Unlike traditional credit card theft, where consumers enjoy statutory liability protections under federal banking regulations, authorized payment scams trick the account holder into sending the wire themselves. Because the legitimate customer authorized the transaction, banks historically refused to reimburse the losses, leaving families financially ruined. Financial platforms adjusting risk models were examined in our review of institutional payment partnerships and stablecoin settlement rules.
The Four Pillar Plan for National Counter Fraud Defense
Friedman proposal outlines a multi-sector defense model that shifts financial security from isolated institutions to a coordinated national perimeter. The plan requires participation across four distinct corporate and government sectors:
- Telecommunications Carriers: Mandating real-time call authentication protocols that identify and block spoofed caller IDs, unauthorized SIM swaps, and suspicious text message routing before calls reach consumer smartphones.
- Big Tech Social Platforms: Requiring social media companies and search engines to verify the legal identity of advertisers running financial promotions, while shutting down deceptive messaging groups within hours of notification.
- Commercial Financial Networks: Establishing shared real-time data exchanges between banks, fintech apps, and cryptocurrency exchanges to trace stolen funds as money hops across institutional accounts.
- Federal Law Enforcement: Creating a unified federal task force with statutory authority to freeze suspicious accounts across multiple institutions without waiting for protracted grand jury subpoenas.
Friedman argued that expecting commercial banks to stop fraud alone is illogical when scams originate on social media apps and travel across telephone networks. If a consumer is groomed on Instagram and contacted through an unvetted voice carrier, the bank enters the sequence only at the final second when money moves. Stopping financial crime demands shutting down the digital pathways that deliver predators to consumer screens. Managing distributed records across corporate networks was detailed in our report on regulators auditing private share ownership records.
The Verafin Weapon: Machine Learning Across Bank Boundaries
Nasdaq strategic interest in this national framework connects directly to its commercial expansion with Verafin. Verafin core strength is its consortium analytics model: analyzing transaction data across thousands of independent financial institutions without violating consumer privacy laws.
In standard banking compliance, Bank A cannot see what happens to funds after they leave its accounts and enter Bank B. Criminals exploit this boundary by bouncing stolen money through four different banks in twenty minutes, knowing that inter-bank inquiries take days of back-and-forth phone calls. Verafin uses encrypted machine learning pipelines to detect movement patterns across its partner network. If an account at a community bank in Ohio initiates a wire to an account in California that was opened two hours earlier and immediately forwards funds to an offshore crypto exchange, Verafin cross-institutional algorithms recognize the mule account structure instantly, pausing settlement across both banks. Expanding this cross-bank intelligence nationally would close the institutional gaps that money launderers exploit. Software systems managing corporate files across distributed networks match architectures we explored when Thally deployed automated knowledge layers across enterprise software suites.
Big Tech Resistance and Common Carrier Immunity
Executing Friedman vision will encounter strong opposition from Silicon Valley platforms and telecommunications carriers. Social media companies generate hundreds of millions of dollars annually selling programmatic ad space to financial promotion companies, many of which use shell entities to bypass basic advertising checks.
Under Section 230 of the Communications Decency Act, internet platforms enjoy broad legal immunity for content posted by third parties. Social media executives argue that screening every advertisement, direct message, and public forum for potential fraud would break user privacy and require impossible moderation overhead. Telecommunications providers cite common carrier principles, claiming they cannot be held responsible for fraudulent phone calls travelling across public copper and fiber wires. Friedman countered that platforms that profit from connecting users must accept legal responsibility for keeping those spaces safe. The Nasdaq chief pointed to recent legislation in the United Kingdom, where social platforms and telephone networks face statutory fines if they fail to remove fraudulent listings, with banks mandated to split the cost of scam reimbursements with the tech platforms where scams originate. Regulatory pressures on large technology platforms were analyzed in our review of state settlements over youth safety protections.
The British Precedent: Mandatory 50-50 Scam Reimbursement
The policy battle in Washington mirrors a dramatic regulatory shift that took effect across the United Kingdom earlier this month. Under updated rules enacted by the British Payment Systems Regulator, British banks are legally mandated to reimburse victims of authorized push payment scams up to £85,000 per incident within five business days.
The British law introduced an unusual mechanism: the sending bank and the receiving bank must split the cost of reimbursement equally, fifty-fifty. This fee structure forced banks to tighten anti-fraud screens: receiving banks can no longer turn a blind eye to suspicious incoming wires because they are legally on the hook for half the stolen money if the receiving account turns out to be a criminal mule. The British government is also advancing legislation that will force social media platforms to reimburse banks for a share of scam losses that originate on their networks. Friedman noted that American regulators at the Consumer Financial Protection Bureau and the Federal Trade Commission are studying the British model closely. If Washington passes similar reimbursement mandates, American banks will face tens of billions in mandatory fraud payouts, giving Wall Street a powerful financial incentive to demand a coordinated national strategy. Restructuring administrative expenses across corporate banking was examined in our report detailing Barclays cutting corporate positions to protect profit margins.
The Privacy Dilemma: Real Time Surveillance Versus Civil Liberties
While the business argument for a national anti-fraud network is compelling, civil liberties organizations warn that uniting telecom, banking, and government databases creates unprecedented surveillance hazards. To trace fraud in real time, algorithms must continuously inspect personal messaging logs, geographic location coordinates, telephone metadata, and retail spending histories.
Privacy advocates point out that centralized financial surveillance systems can be abused. An algorithm designed to spot unauthorized money transfers can easily be repurposed to monitor political donations, track union organizing funds, or flag controversial personal purchases. If an automated security engine mistakenly freezes a citizen account based on a false-positive suspicion, the affected individual can find themselves locked out of their life savings with zero clear appeal process. Friedman acknowledged that any national strategy must include strict data privacy vaults: using zero-knowledge cryptographic proofs to verify identities and spot fraud patterns without giving government agencies or private tech platforms open access to personal consumer ledgers. Ethical boundaries governing automated systems were documented in our coverage of testing safety perimeters in new software platforms.
The Final Warning for Capitol Hill
Adena Friedman call for a national anti-fraud strategy proves that the global financial sector has reached a tipping point. Financial crime has expanded beyond a localized law enforcement nuisance; it has become an industrial threat that siphons hundreds of billions of dollars out of legitimate economies every year, funding narcotics cartels, human trafficking rings, and rogue foreign states.
The notion that private banks can protect citizens while tech platforms and telephone networks remain passive spectators is an obsolete fantasy. If Washington fails to enact comprehensive federal legislation that forces all sectors to share security intelligence, the fraud epidemic will continue to accelerate, destroying consumer trust in digital payments. As Nasdaq and Verafin demonstrate what coordinated software intelligence can accomplish, the responsibility rests with lawmakers on Capitol Hill to provide the legal backing required to build a national defense. In the digital economy, economic security cannot be preserved by isolated corporate firewalls; it demands a unified perimeter that defends the integrity of commerce for everyone. Corporate performance pressures across the technology sector were analyzed in our report on Wall Street corporate earnings pressure, while public administration risks were explored when automated software programs overwhelmed public services.
Read More on TechRobust:
Inioluwa Ademidun
 LinkedIn
Inioluwa Ademidun
Expertise:African Tech Ecosystem, Early-Stage Startups, Emerging Market Dynamics, Venture Capital & Tech Reporting, Product Management
Award:TechRobust Contributor of the Year 2025
Inioluwa is a Senior Product Manager by day and an investigative technology reporter by night, bridging the gap between scalable software architecture and high-impact journalism. She delivers deep-dive analysis on venture-backed founders, regulatory shifts, and grassroots tech ecosystems across Africa and global emerging markets.